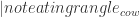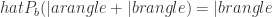Category Archives: Physics

In memory of Sean Barrett

When I was a budding young PhD student, trying to find my way into the world of academia and theoretical physics, there was a small group of people who guided me, stood up for me, collaborated with me, provided a guiding hand, and acted as wonderful, compassionate friends. One of those people was Sean Barrett, who was killed last week in a senseless driving accident involving a young man with a stolen vehicle.

Sean was one of the brightest young men I’ve ever met, and by the age of his death, 36, had already made a vast contribution to my field of quantum computing. He was destined to become one of the big names in this exciting and future-defining field.

Most notably, he made significant contributions to optical quantum computation, quantum error correction and fault tolerance, and topological and cluster state quantum computation. This included two papers with me on cluster state preparation and atomic ensemble quantum computation. He had a stellar career, involving many prestigious positions, including holding a fellowship with the Royal Society.

I’ll never forget the assistance Sean provided me in my early career and the friendship and laughs he brought with it. I feel eternally grateful for the role he played in my life.

He will be sadly missed by his friends, family and colleagues, who all knew him as a brilliant young mind with a magnetic and cheerful personality. The world has been robbed of a truly outstanding young man with much to contribute.

I wish his family and friends all the best.

New paper: Optical quantum computing with photons of arbitrarily low fidelity and purity

Download full text here.

Linear optics quantum computing (LOQC) is a leading candidate for the implementation of large scale quantum computers. Here quantum information is encoded into the quantum states of light and computation proceeds via a linear optics network. It is well known that in such schemes there are stringent requirements on the spatio-temporal structure of photons – they must be completely indistinguishable and of very high purity. We show that in the Boson-sampling model for LOQC these conditions may be significantly relaxed. We present evidence that by increasing the size of the system we can implement a computationally hard algorithm even if our photons have arbitrarily low fidelity and purity. These relaxed conditions make Boson-sampling LOQC within reach of present-day technology.

Many worlds and the interpretation of quantum mechanics

This post is on quantum mechanics, but is intended to be understandable by anyone. The small amount of mathematical notation that I introduce should be fairly digestible to anyone without a physics background.

A couple of nights ago I had a dinner table conversation with a fellow physicist, who raised the highly emotive, almost religious issue of the interpretation of quantum mechanics. For the non-physicists, quantum mechanics has some very unusual properties that we are not used to encountering in the world around us. The most well known of these unusual properties is the notion of a superposition, whereby something can assume multiple states simulatenously. A state is simply a property of a system. For example, the position of a particle is represented by a state. A superposition in this context means that the particle is in multiple positions simultaneously. Obviously this is very counterintuitive indeed. This, as well as numerous other counterintuitive properties of quantum mechanics give rise to the argument over the interpretation of quantum mechanics. That is, how do we reconcile such strange behavior with our inherent human desire for cartoon descriptions of everything.

Mathematical background (for non-mathematicians and non-physicists)

Let me now expand on this. I’ll do this by introducing the mathematical tools that physicists actually use, but in a way that can hopefully be understood to anyone without such a background.

Suppose we have a system, which we will label A. This could be anything – a particle, a cow, a person, a banana. Using quantum mechanical notation we will represent the state of a system as |s rangle_A, where s represents the actual state, and the subscript A denotes the system we are referring to. For example, suppose we have a two-level cow, which can be in one of two states – it can be eating, or not eating. The mathematical descriptions of these two states are |eating rangle_{cow} and |not eating rangle_{cow}. In quantum mechanics we denote a superposition using a ‘+’ symbol. So a superposition of two states a and b is just denoted |a rangle+|b rangle.

This completes the quantum mechanical notations we use for representing the states of systems. Next we’ll turn our attention to the evolution (i.e. the dynamics) of a quantum system. In quantum mechanics there are precisely two (or possibly just one, as we will discuss later) types of dynamics. The first is so-called unitary evolution. The technical definition of this is irrelevant here. Just think of it as an operation that maps one state to another. For example the unitary evolution describing a two-level cow that is initially standing around and then decides to have dinner, is described by hat{U}|not eating rangle_{cow}to |eating rangle_{cow}, where hat{U} denotes the unitary evolution operation.

The second type of evolution that is possible is the so-called projective measurement. As the name suggests, this type of evolution takes place when we measure a system. As an example, suppose we start with a system in a superposition of two states, |a rangle+|b rangle, and we measure it to establish whether the system is in state a or state b. When we perform this measurement we always get either one answer or the other. Our measurement device never says ‘you have a superposition of a and b‘. This is why we don’t observe quantum mechanical effects in the world around us. So the question now is, if we have a superposition, which measurement result do we get? The answer is that our result is random. Truly random, in the sense that it is impossible, even in principle, to predict it. So 50% of the time our measurement device will say ‘you have a‘, and the other 50% of the time it will say ‘you have b‘. After the measurement, the state of the system collapses (according to the standard interpretations of quantum mechanics) into either |a rangle or |b rangle. Notice that after a projective measurement, the system is no longer in a superposition. In other words, the strange quantum mechanical properties dissapear. To describe this mathematically we’ll introduce corresponding measurement operations. If we perform a measurement and get outcome x, we denote the measurement operation as hat{P}_x. So, referring to the discussed example we have

hat{P}_a(|a rangle+|b rangle)=|a rangle
hat{P}_b(|a rangle+|b rangle)=|b rangle

It turns out that this kind of evolution cannot be described by the unitary evolutions I mentioned before.

The measurement problem

The previous discussion gives rise to an obvious question. What constitutes a measurement? We know from numerous experiments that if we have an isolated system of say, atoms interacting with one another, then the system evolves unitarily. It is only when we look at it that this projective evolution takes place. In general, isolated small systems evolve unitarily, but as soon as they interact with a macroscopic system they undergo projective dynamics. The distinction seems very arbitrary. What is it that actually causes this transition from one type of dynamics to another? This is the so-called ‘measurement problem’, and is one of central points of contention in the interpretation of quantum mechanics.

Many worlds

One interpretation of quantum mechanics, which resolves the measurement problem, is the so-called ‘many worlds’ interpretation, which I will now describe. Suppose we begin with two systems, an observer and an atom. We assume the atom is in a superposition of two states, 0 and 1. The observer could be you or I, and can assume one of three possible states: ‘doing nothing’, ‘I think I measured 0’ and ‘I think I measued 1’. We’ll assume the observer is initially in the ‘doing nothing’ state. So, the state of the entire system can be expressed

|nothing rangle_{observer}(|0 rangle_{atom}+|1 rangle_{atom})

Expanding the brackets this is equal to

|nothing rangle_{observer}|0 rangle_{atom}+|nothing rangle_{observer}|1 rangle_{atom}

Now we are going to apply a unitary evolution that performs the following mapping

hat{U} |nothing rangle_{observer}|0 rangle_{atom} to |I measured 0 rangle_{observer}|0 rangle_{atom}
hat{U} |nothing rangle_{observer}|1 rangle_{atom} to |I measured 1 rangle_{observer}|1 rangle_{atom}

In other words, this evolution maps an idle observer to the state where he believes he has measured whatever the respective state of the atom is. So what happens when we apply this evolution to the initial state?
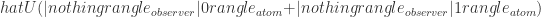
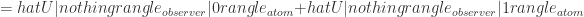
hat{U}(|nothing rangle_{observer}|0 rangle_{atom}+|nothing rangle_{observer}|1 rangle_{atom})
=hat{U}|nothing rangle_{observer}|0 rangle_{atom}+hat{U}|nothing rangle_{observer}|1 rangle_{atom}
=|I measured 0 rangle_{observer}|0 rangle_{atom}+|I measured 1 rangle_{observer}|1 rangle_{atom}

We now have a state which is a superposition of the atom being in state 0 and the observer thinking that the atom is in state 0, and the atom being in state 1 and the observer think the atom is in state 1. This is a so-called entangled state, a superposition where the states of distinct systems are correlated within the superposition. Entanglement is another one of the quirky features of quantum mechanics, which gives rise to all sorts of strange phenomena. But I won’t go into that now.

With a little bit of algebraic rearrangement, it can easily be seen that this state is equal to

|I measured 0 rangle_{observer}hat{P}_0(|0 rangle_{atom}+|1 rangle_{atom})
+|I measured 1 rangle_{observer}hat{P}_1(|0 rangle_{atom}+|1 rangle_{atom})

In this expression we have a superposition of an observer who thinks he measured a 0 and 1 respectively, and the state of the atom is described by the respective projection. Note that we have not inserted projection operators explicitly at any stage, it arises naturally as a result of the entanglement between the observer and the system he is measuring. This is how the ‘many worlds’ interpretation of quantum mechanics arises. There is no such thing as a projective measurement. Instead, whenever we (an observer) become entangled with a system we enter a superposition with it. Note that from the view-point of a particular term in the superposition, projective measurement has taken place. Thus, according to this interpretation, the reason we observe projective dynamics in the real world is because we are simply one of the terms in the superposition.

This interpretation resolves several issues. First, there is no arbitrary scale at which interactions become projective. Instead it arises very naturally as a result of our entanglement with that which we are observing. Second, the laws of physics are once again completely deterministic, since these non-deterministic projections no longer exist. Unfortunately, this interpretation also raises a somewhat depressing and overwhelming possibility. That is, we are simply one term in an almost infinitely large superposition of parallel worlds. Every time you look at an atom and observe a 0, there’s another you in a parallel world that observed a 1. For some reason I find this quite distressing.

Scholarships for PhD students at Macquarie University, Sydney

I’d appreciate if you could let any interested students know of the following PhD opportunities:

Limited scholarships are available for several PhD students at Macquarie University (Sydney, Australia) in the field of theoretical quantum physics. Students will work with A/Prof. Alexei Gilchrist and Dr. Peter Rohde on topics including quantum computing, quantum information theory, quantum optics, quantum state and process tomography, and quantum random walks. The research will be part of the ARC Centre for Engineered Quantum Systems (http://equs.org). Applicants should have a degree in mathematics, physics or engineering and have a good understanding of mathematics and physics. Interested applicants should contact A/Prof. Alexei Gilchrist (alexei@ectropy.info) or Dr. Peter Rohde (dr.rohde@gmail.com) with a resume. Applications will be considered upon receipt.

Do we need quantum cryptography?

Quantum cryptography is all the hype. Everyone’s talking about it. Scientists are competing to do it over the longest possible distances, with the highest possible bit-rates and even to put it into orbit on satellites. In this post I’d like to explain what quantum cryptography is and compare it to classical cryptography. Then I’ll tell you why I think it’s all a waste of time and money, and why the same money should instead be spent on other quantum technologies like quantum computing.

What is cryptography?

Cryptography is the science of obfuscating messages so that only an intended recipient can read it, and no one else can. It’s been around for millennia in early forms. First attempts at cryptography included simple substitution ciphers, whereby we swap around the letters in a message to scramble it. For example, we replace the letter ‘A’ with the letter ‘P’, the letter ‘Z’ with the letter ‘C’, and so on. The intended recipient knows in advance what the substitution is (the ‘key’), and can easily reverse it. But to someone who doesn’t know the correct substitutions, they see gibberish. Modern cryptography is nothing more than a much more mathematically advanced approach to achieving the same goal. The simple substitution cipher I mentioned can trivially be broken using a letter-frequency analysis. We know that in the English language different letters appear with different frequencies. The letter ‘E’ appears much more often than the letter ‘X’. Thus, by carefully analysing the frequencies of different letters, we can soon figure out what the substitution is. This is called cryptanalysis. During World War II the Nazis used the Enigma machine to encrypt their communications. This was famously cracked by Alan Turing, arguably tipping the balance in the war. Modern codes eliminate these kinds of attacks using advanced mathematics, which creates codes much harder to cryptanalyse and reverse.

What is quantum cryptography?

Quantum cryptography is an approach to cryptography based on the laws of quantum mechanics. There are various protocols, but all ultimately rely on the truly random nature of the measurement of quantum mechanical systems. This randomness is used to obscure information in a way that cannot be reversed, even if the line of communication is eavesdropped. Quantum cryptography is ‘provably secure’ and immune to cryptanalysis. That is, we can mathematically prove that even if an eavesdropper has full access to the communication between two parties, it is theoretically impossible for them to extract the hidden message. This is a bold claim, and the reason quantum cryptography attracts so much interest. Several companies have released commercial quantum cryptography products, available to buy off-the-shelf for private use.

Why do we need quantum cryptography?

The reason quantum cryptography has attracted particular interest is that it is secure even in the advent of quantum computing. Quantum computers – computers based on the laws of quantum mechanics – are exponentially faster than classical computers for some applications. One of the best known applications for quantum computers is their ability to crack RSA, a public-key encryption protocol, which is the mainstay of modern secure internet communication. Every time you type in your credit card online it’s protected by RSA encryption. And while there are no known classical algorithms that compromise RSA, there is a well known quantum algorithm that can easily crack it, known as Shor’s algorithm. This is not the case for quantum cryptography. Quantum cryptography is secure even if the eavesdropper has a quantum computer at their disposal. Thus, proponents tout that quantum cryptography is necessary to future-proof our cryptographic protocols against quantum computers.

What are the limitations of quantum cryptography?

While quantum cryptography is provably secure on paper, when we build it it’s no longer on paper, but a physical device with imperfections. These imperfections can compromise the security of the protocol and undermine its status as ‘provably secure’. There have been numerous cases where scientists have constructed a quantum cryptographic device and claimed it to be provably secure, only to have it debunked because the experiment they built in the lab didn’t perfectly implement what was written on paper. For this reason, if someone approached me and asked for security advice, I would strongly advise against employing quantum cryptography.

Why don’t we need quantum cryptography?

As discussed, quantum cryptography is provably secure on paper, but not necessarily so once it’s built in the lab. We are presented with two alternatives. The first is to continue pursuing quantum cryptography, trying again and again to build physical devices that are provably secure. The second is to abandon it and go back to classical cryptography. Why do the latter when I’ve already said that classical cryptography can be compromised by quantum computers? Because not all classical cryptographic protocols are compromised by quantum computers. The RSA algorithm, which we heavily employ today, is compromised because quantum computers can solve the integer factorisation problem, upon which RSA is based. However, there are more recent classical protocols that are based on harder mathematical problems, which quantum computers are strongly believed to not be able to solve. One contender is the McEliece protocol. This is a public-key protocol, like RSA, and could therefore be applied to the same applications as RSA. However, McEliece is based on a so-called NP-hard problem. While this is not provably secure as quantum cryptography is, scientists have very strong reason to believe that NP-hard problems cannot be solved by quantum computers. If this mathematical statement is correct, then McEliece and other similar protocols would be viable protocols in a post-quantum computer world. The advantage of adopting a post-quantum classical cryptographic protocol as opposed to a quantum cryptographic protocol is that we don’t need to build a whole new quantum infrastructure for the internet and other forms of communication – we can continue to use the same infrastructure and just update our software, with no additional cost. A software update is certainly much easier than putting quantum satellites into space.

What should we instead invest in?

In my opinion, post-quantum classical cryptographic protocols are actually more secure than quantum cryptographic protocols, and the cost overhead is zero. As such, I see little reason to continue investing huge amounts of money into quantum cryptography. I’d rather see the money invested into other quantum technologies like quantum computing, which will have significant genuine benefits over classical computing that could be achieved in no other way.

Now that I’ve said all this I’m going to upset a lot of high-profile people and no one in the field of quantum cryptography is ever going to offer me a job again.

My Academic Lineage

From the Mathematics Genealogy Project:

Peter Rohde (University of Queensland, 2008) was a student of
Tim Ralph (Australian National University, 1996) who was a student of
Craig Savage (University of Waikato) who was a student of
Dan Walls (Harvard University, 1969) who was a student of
Roy Glauber (Harvard University, 1949) who was a student of
Julian Seymour Schwinger (Columbia University, 1939) who was a student of
Isidor Isaac Rabi (Columbia University, 1927) who was a student of
Albert Potter Wills (Clark University, 1897) who was a student of
Arthur Gordon Webster (Universität Berlin, 1890) who was a student of
Hermann Ludwig Ferdinand von Helmholtz (Universität Berlin, 1842) who was a student of
Johannes Peter Müller (Rheinische Friedrich-Wilhelms-Universität Bonn, 1822) who was a student of
Karl Asmund Rudolphi (Ernst-Moritz-Arndt-Universität Greifswald, 1795) who was a student of
Christian Ehrenfried von Weigel (Georg-August-Universität Göttingen, 1771) who was a student of
Johann Christian Polykarp Erxleben (Georg-August-Universität Göttingen, 1767) who was a student of
Abraham Gotthelf Kästner (Universität Leipzig, 1739) who was a student of
Christian August Hausen (Martin-Luther-Universität Halle-Wittenberg, 1713) who was a student of
Johann Andreas Planer (Eberhard-Karls-Universität Tübingen, 1709) who was a student of
Johann Pasch (Martin-Luther-Universität Halle-Wittenberg, 1683) who was a student of
Michael Walther, Jr. (Martin-Luther-Universität Halle-Wittenberg, 1661) who was a student of
Johann Andreas Quenstedt (Martin-Luther-Universität Halle-Wittenberg, 1644) who was a student of
Christoph Notnagel (Martin-Luther-Universität Halle-Wittenberg, 1630) who was a student of
Ambrosius Rhodius (Martin-Luther-Universität Halle-Wittenberg, 1610) who was a student of
Melchior Jöstel (Martin-Luther-Universität Halle-Wittenberg, 1600) who was a student of
Valentin (Valentinus Otho) Otto (Martin-Luther-Universität Halle-Wittenberg, 1570) who was a student of
Georg Joachim von Leuchen Rheticus (Martin-Luther-Universität Halle-Wittenberg, 1535) who was a student of
Nicolaus Copernicus (Uniwersytet Jagielloński, 1499)

New paper: Increasing the dimensionality of quantum walks using multiple walkers

Download the full article here.

We show that with the addition of multiple walkers, quantum walks on a line can be transformed into lattice graphs of higher dimension. Thus, multi-walker walks can simulate single-walker walks on higher dimensional graphs and vice versa. This exponential complexity opens up new applications for present-day quantum walk experiments. We discuss the applications of such higher-dimensional structures and how they relate to linear optics quantum computing. In particular we show that multi-walker quantum walks are equivalent to the BosonSampling model for linear optics quantum computation proposed by Aaronson & Arkhipov. With the addition of control over phase-defects in the lattice, which can be simulated with entangling gates, asymmetric lattice structures can be constructed which are universal for quantum computation.

New paper: Quantum walks with encrypted data

Download the full article here.

In the setting of networked computation, data security can be a significant concern. Here we consider the problem of allowing a server to remotely manipulate client supplied data, in such a way that both the information obtained by the client about the server’s operation and the information obtained by the server about the client’s data are significantly limited. We present a protocol for achieving such functionality in two closely related models of restricted quantum computation — the Boson sampling and quantum walk models. Due to the limited technological requirements of the Boson scattering model, small scale implementations of this technique are feasible with present-day technology.

New paper: A 2D Quantum Walk Simulation of Two-Particle Dynamics

This paper was recently published in Science. Download the full article here.

Multi-dimensional quantum walks can exhibit highly non-trivial topological structure, providing a powerful tool for simulating quantum information and transport systems. We present a flexible implementation of a 2D optical quantum walk on a lattice, demonstrating a scalable quantum walk on a non-trivial graph structure. We realized a coherent quantum walk over 12 steps and 169 positions using an optical fiber network. With our broad spectrum of quantum coins we were able to simulate the creation of entanglement in bipartite systems with conditioned interactions. Introducing dynamic control allowed for the investigation of effects such as strong non-linearities or two-particle scattering. Our results illustrate the potential of quantum walks as a route for simulating and understanding complex quantum systems.